
Capabilities come from configured tools and information
ServiceNow's AI-agent build guide describes agents through identity, request descriptions, instructions, tools, and security settings. Tools can include script tools, subflows, and knowledge retrievers. They are not interchangeable “skills”: each adds a data or action path that needs its own purpose and permission review.
ServiceNow's tool guidance recommends tools for a specific, discrete task. A good description says what it does, when to use it, when not to use it, and any domain terms it needs. For a support workflow, “retrieve warranty eligibility” and “create a warranty-review task” are easier to govern than one tool called “handle warranties.”
Treat access as part of the capability
Decide separately who can invoke the agent and what records each tool can read or change. ServiceNow warns that a GlideRecord script tool bypasses table-level ACLs; GlideRecordSecure enforces those checks. This is exactly why an action's code path and its access boundary both belong in the review.
Test normal inputs, missing fields, unauthorized requesters, tool errors, and cases requiring human review. Inspect the response and action request, then verify the ticket, task, entitlement, or external system. A response that says “done” is not proof that the underlying work is correct.
Inspect eesel support capabilities with CLI
For an eesel helpdesk teammate, eesel CLI lets people work through a terminal, while scripts and coding agents such as Claude Code, Codex, and Cursor consume JSON from the same eesel workspace and teammate as the dashboard. That makes a concrete support capability, such as proposing a return, inspectable alongside the dashboard before a team widens its scope. ServiceNow AI Agent Studio remains where ServiceNow tools are configured.
For example, before expanding a teammate from drafting shipping guidance to proposing a return, a support owner can ask a coding agent to inspect the selected teammate's integrations and instructions. That report should identify whether the return boundary and human-review rule exist. It should not add a new integration, change an action, or make a write during inspection.
With Node.js 18.17 or newer, make the target explicit:
npx @eesel/cli login
npx @eesel/cli whoami
TARGET_EESEL_AGENT="paste-agent-id-or-name-here"
npx @eesel/cli integrations --agent "$TARGET_EESEL_AGENT"
npx @eesel/cli instructions --agent "$TARGET_EESEL_AGENT"
npx @eesel/cli approvals --agent "$TARGET_EESEL_AGENT"
After approval, use --dry-run for a supported change. Keep unrelated actions contained before a representative test chat, then inspect Activity and held approvals. Confirm the actual ticket or connected-system result after controlled rollout. The CLI can make this evidence repeatable; it does not substitute for the owner who authorizes a consequential action.
Add only the capability you can own
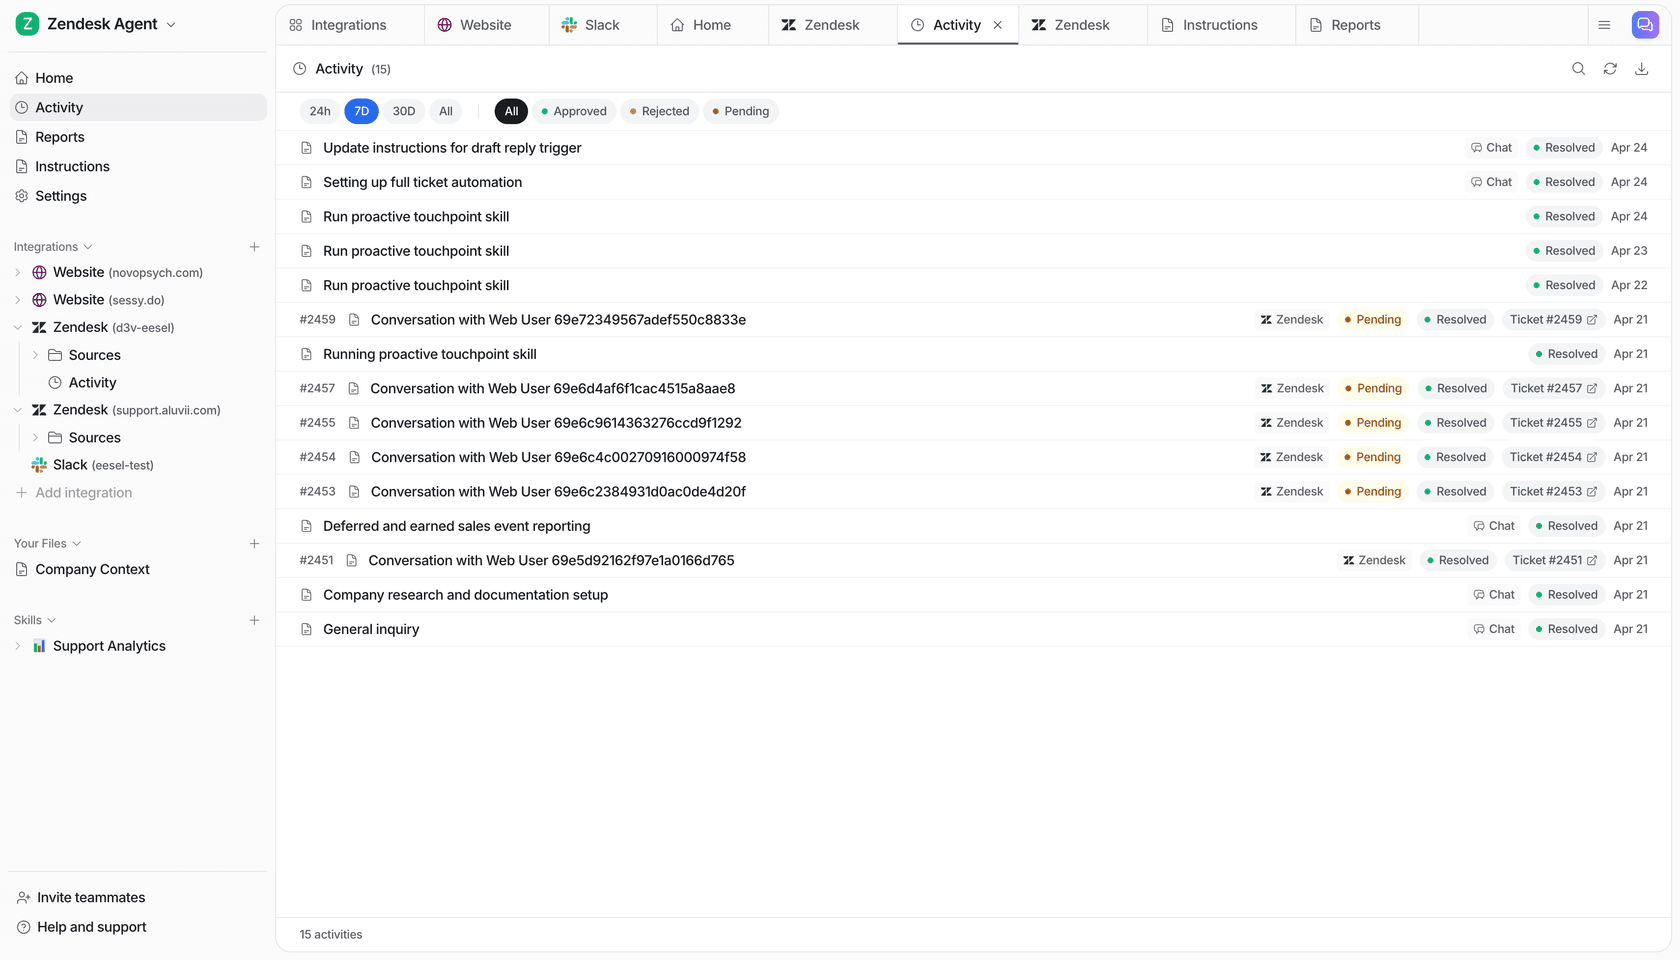
The eesel Activity page shows a work list and filters for approved, rejected, and pending items.
Try eesel to inspect one support capability before giving a teammate a wider customer-facing role.
Frequently asked questions
What are AI-agent skills in ServiceNow?
An AI agent uses configured tools and information to complete its defined task. ServiceNow describes tools such as script tools, subflows, and knowledge retrievers; their purpose and access shape the capability an agent has.
Why should a tool have a narrow purpose?
ServiceNow advises defining tools for a specific discrete task and describing their function, when to use them, when not to use them, and relevant terms. Narrow scope improves testing and reduces unnecessary access.
How do access controls apply?
Teams must control who can invoke an agent and what its tools can access. ServiceNow specifically warns that a GlideRecord script tool bypasses table ACLs; GlideRecordSecure enforces ACL checks.
What should a tool test cover?
Cover correct inputs, absent or malformed fields, authorization failure, tool error, repeated requests, and the expected human handoff. Verify any resulting record or external action separately.
Can one skill safely do everything?
A broad capability makes tool selection, permission review, and troubleshooting harder. Keep read, draft, approval, and write steps distinct where their risk and owners differ.